Encryption made simple,
secure, and
automated
Manage, rotate, and protect your cryptographic keys across
clouds and teams - all from one secure, compliant platform.
Enterprise-Grade Encryption
Hardware-Isolated Keys (TEE)
True Zero-Knowledge Architecture
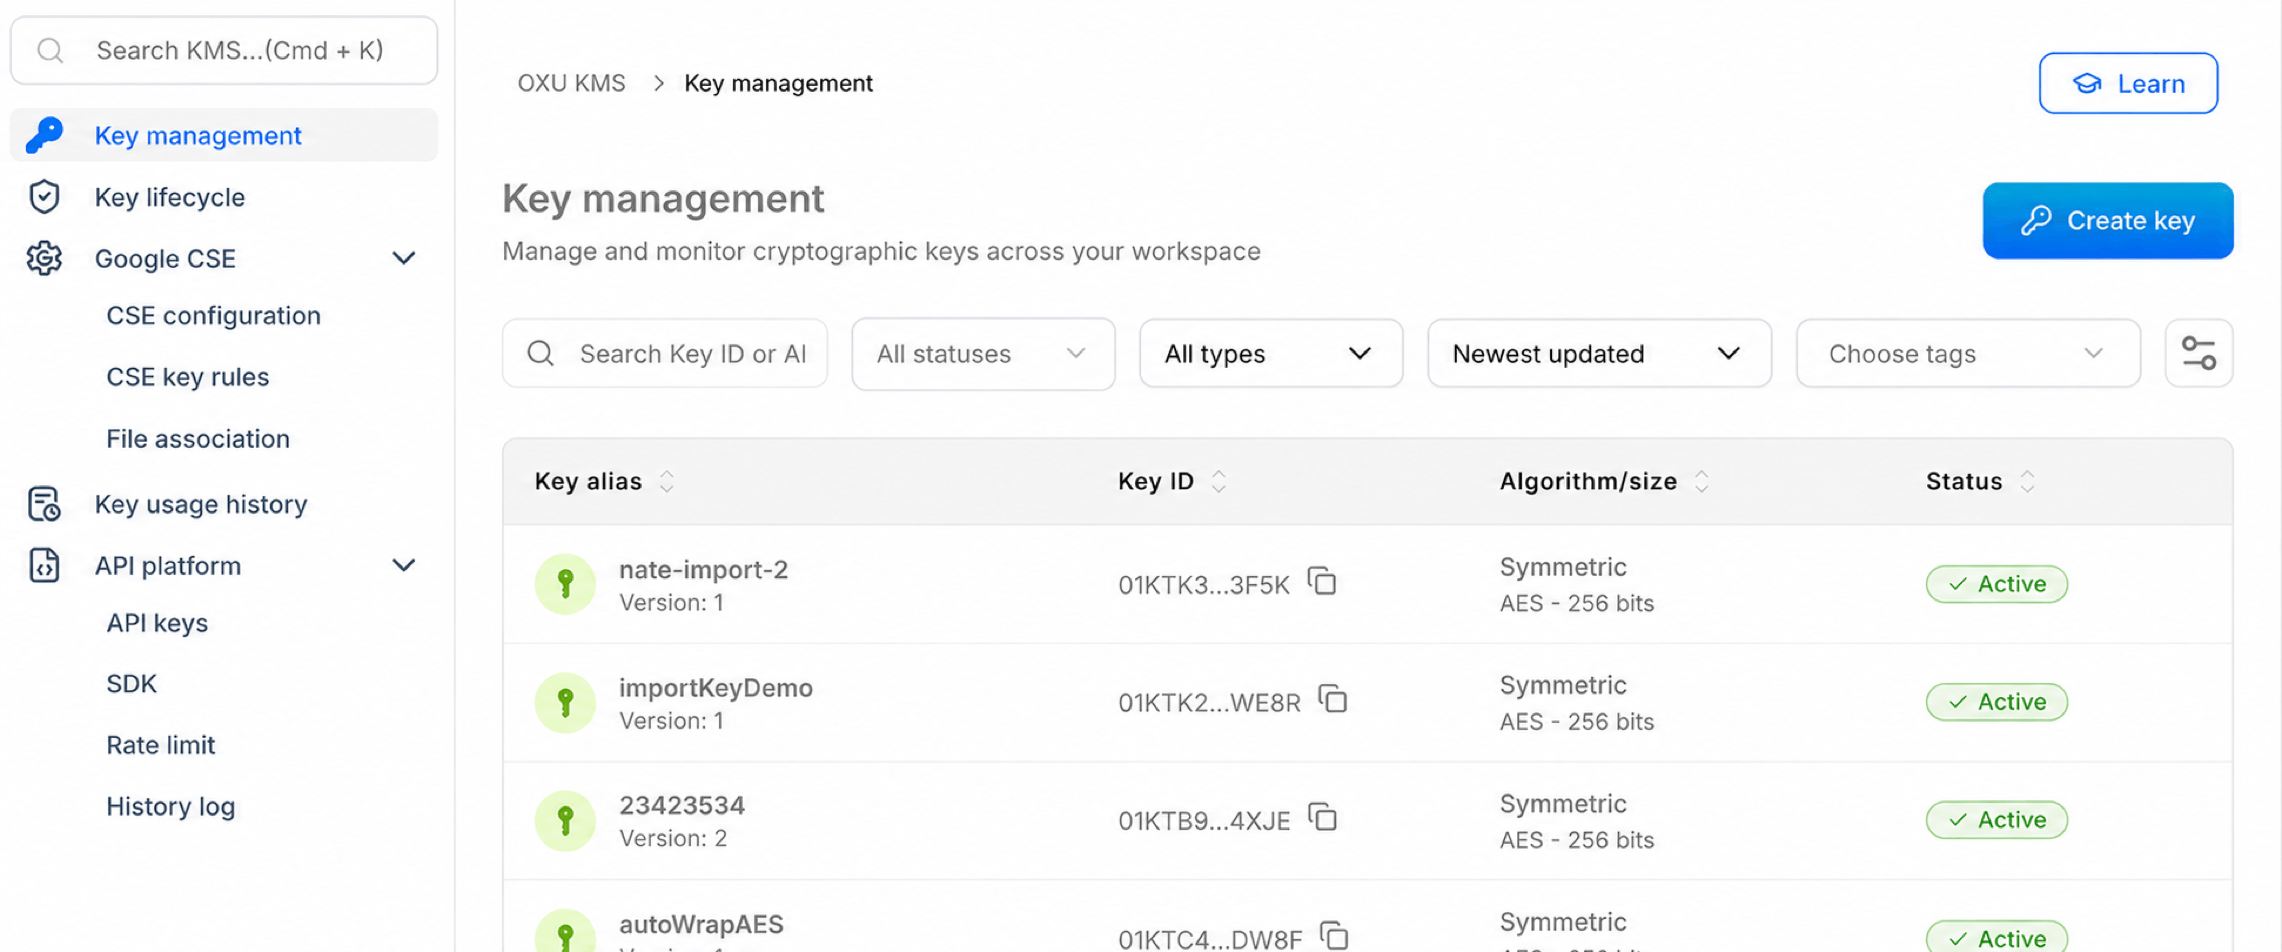

Eliminate key sprawl and human error across teams

Hard isolation per workspace to prevent blast-radius breaches

Deploy without refactoring existing Google Workspace workflows
How it works
Follow three simple steps to secure, manage, and automate your encryption keys — all from one intuitive, enterprise-grade platform.
1
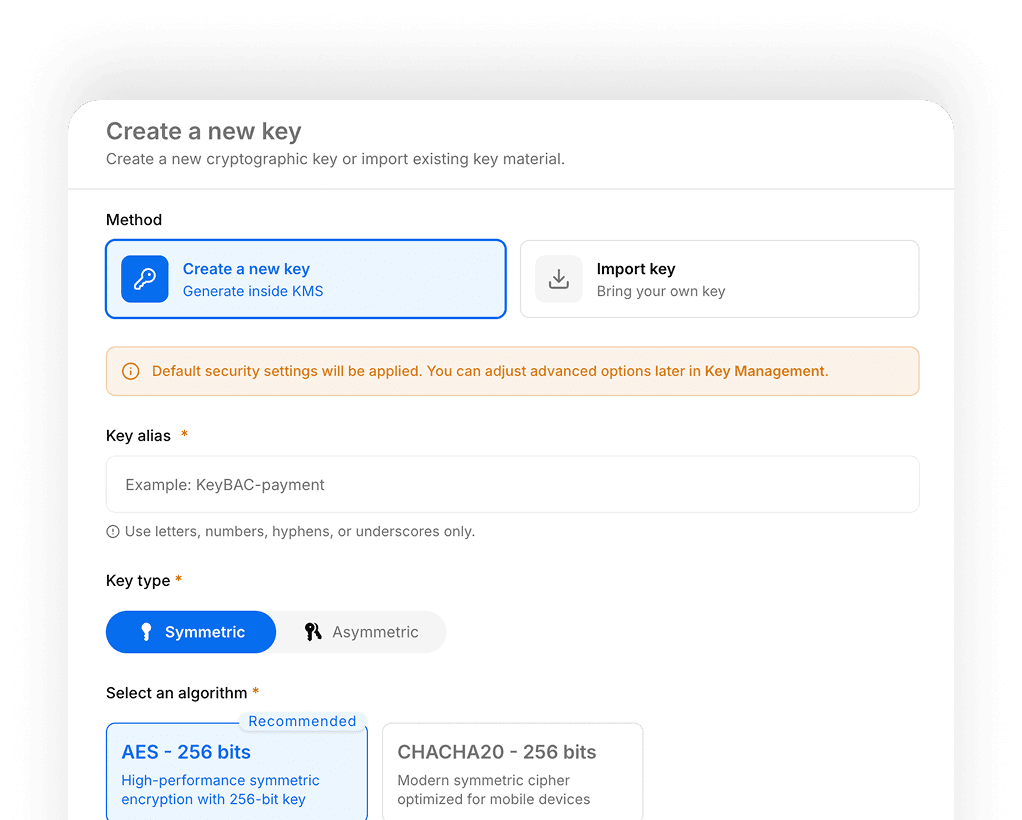
Create keys in second
Choose algorithm, key size, and permissions.2
Encrypt everywhere
Apply to workloads, APIs, or storage.3
Automate rotation & audit
Schedule rotations and monitor instantly.Use cases

Centralized key lifecycle management with enforced rotation policies

Create, access, and collaborate on client-side encrypted files seamlessly

Automated auditing, monitoring, and regulatory compliance reporting
Security & compliance
Enterprise-grade security built into every layer

Your keys remain fully under your control. OXU KMS never accesses or repurposes.

Keys stay inside Trusted Execution Environments. No plaintext leaves.

All cryptographic actions are auditable. Logs are securely retained.
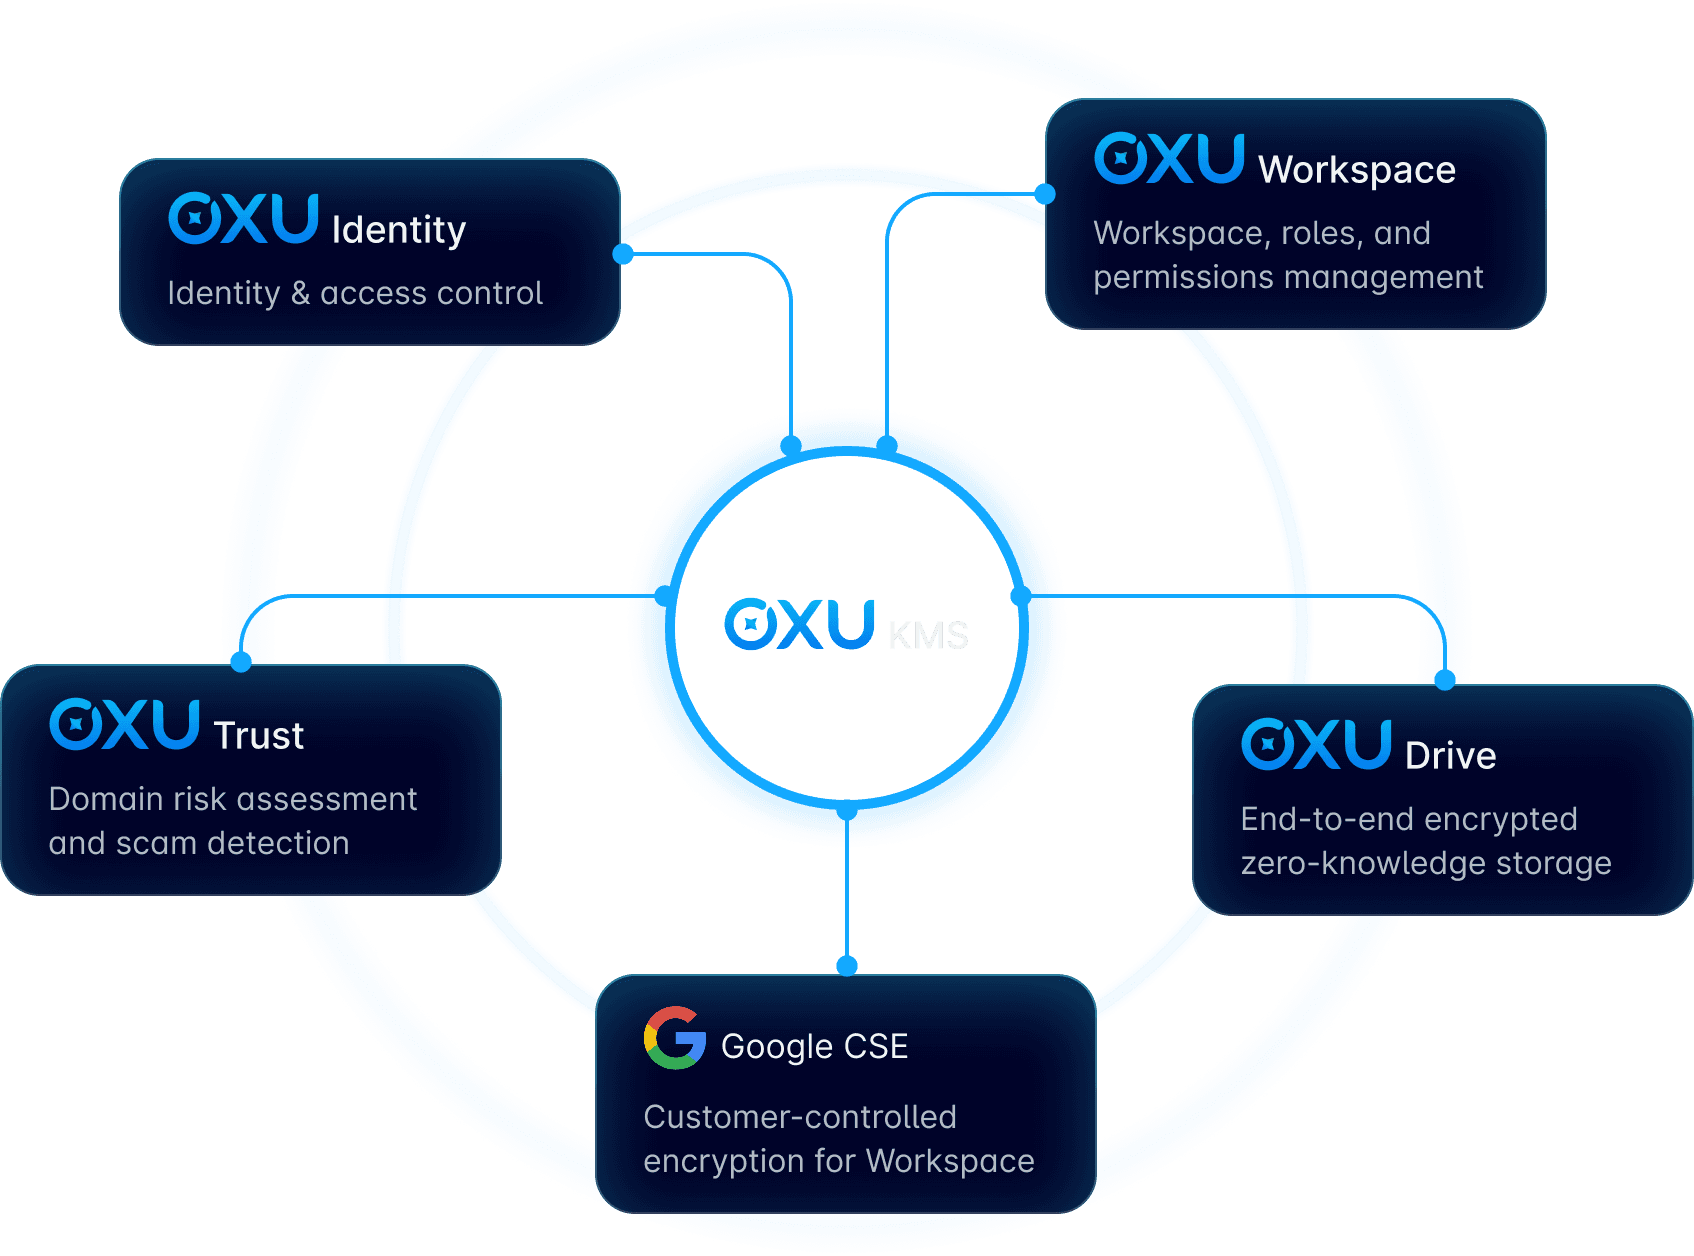
Enterprise integration ecosystem
Built to integrate seamlessly with enterprise cloud services and Google Workspace.
Want to learn more about OXU KMS?
Check out our Frequently Asked Questions to discover more.
Ready to secure your enterprise data?
Join security-conscious organizations managing their Google CSE keys with confidence
and full control across their organization.